Which Agent Actions Need a Human Approval Step
Approve actions based on their consequences, not every step an agent takes. Sort the workflow into read-only, reversible and hard-to-undo actions before building.
An agent that finds an invoice and an agent that pays it are doing very different jobs. Both may sit inside the same accounts payable workflow, but they should not have the same permission to act.
Requiring approval for every lookup, calculation and draft can leave your team doing almost as much work as before. Letting every action happen automatically creates a different problem: a small misunderstanding can become a payment, a customer promise or a damaged record.
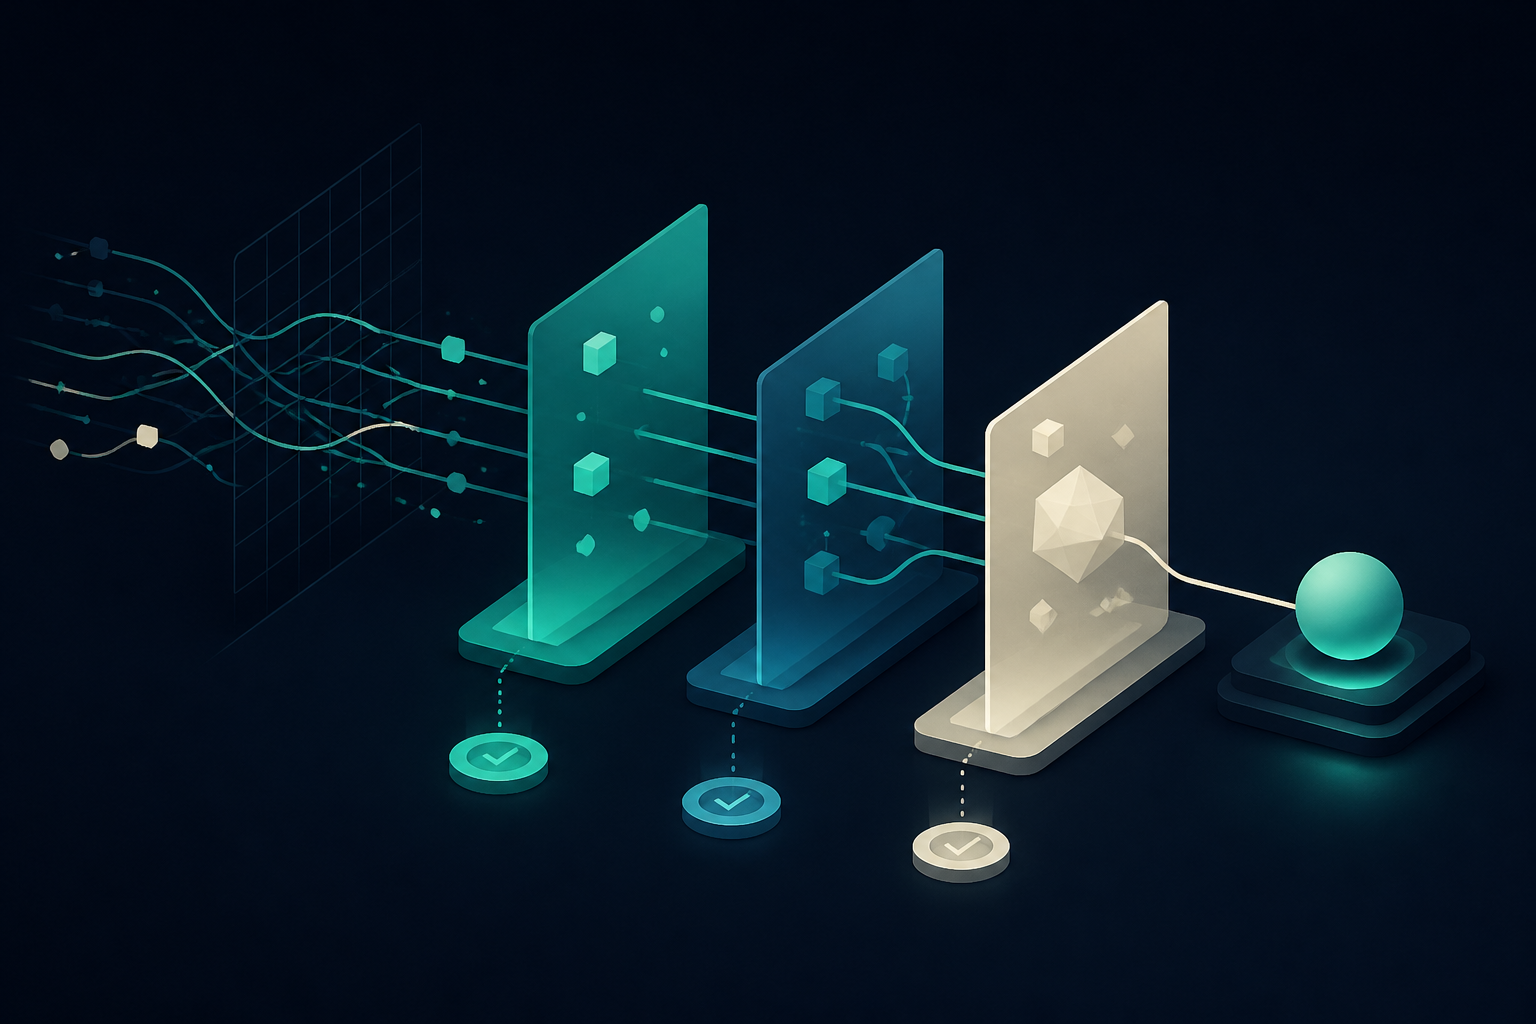
The practical starting point is to classify each action by its consequences. Read-only actions, reversible actions and actions that are hard to undo need different controls. Put human approvals on the last group first. Consider relaxing them only when testing and operating evidence support a narrower rule.
Sort actions, not whole workflows
Calling a workflow “low risk” is too broad to guide a build. A support request might involve finding a policy, drafting a response, changing an account and sending an email. Each step needs its own decision.
Before building, list the actions the agent would take. Use specific verbs: read, search, draft, create, update, send, delete, refund. “Handle customer requests” is not specific enough.
Then tag each action with one of three groups:
- Read only: Retrieves or analyzes information without changing the source or communicating externally.
- Reversible: Makes a change that can be reliably undone, with limited consequences while it is in place.
- Hard to undo: Creates an external commitment, moves money, exposes information or changes something whose consequences cannot easily be reversed.
Classify by the real effect, not the button label. Changing a record might be reversible if it updates a private working note. Changing a customer's delivery address after dispatch may not be.
This action list becomes a practical specification for what the agent may do alone and where it must stop.
Let read-only work proceed within boundaries
Searching an approved handbook, finding an order and extracting fields from an invoice are usually good candidates for automation without individual approvals.
In a hypothetical invoice workflow, the agent could read the uploaded document, extract the supplier and amount, and compare those details with a purchase order. A person does not need to approve each lookup.
Read only does not mean risk free. An agent can retrieve the wrong record, misunderstand a policy or access information it should not see. Its access should therefore be limited to the information needed for the task.
There is also a difference between reading information and sharing it. Looking up an account balance internally is read only. Emailing that balance to someone is a separate action with a separate risk.
For this group, focus on access permissions, source quality and checks on the result. If the agent cannot find the right policy or match the right customer, it should stop or ask for help rather than guess.
Make reversibility a real operating capability
Drafting an email without sending it, adding an internal label or creating a task may be reversible actions. They can often proceed automatically if the scope is limited and the team can inspect what happened.
But “we could fix it later” is not enough. A useful reversal needs:
- A record of what changed and what was there before.
- A reliable way to restore the previous state.
- A person responsible for handling mistakes.
- No significant downstream effect before the mistake can be corrected.
Consider a hypothetical agent that tags a support ticket as “billing.” If the tag simply organizes a queue, correcting it may be straightforward. If that tag triggers a collection notice, the action belongs in the hard-to-undo group.
The same applies to record changes. Updating a draft contact record is different from replacing the billing details used by another system.
Test the undo path before granting permission. If nobody can explain how to restore the previous state, treat the action as hard to undo until that gap is resolved.
Put approval before the consequential action
Sending money, emailing a customer and changing an important business record should start with human approval. Deleting data, publishing content and changing access permissions also deserve close attention.
An email can be followed by a correction, but the original message has already been read or forwarded. Correcting a mistake later is not the same as reliably undoing its effects.
Place approval immediately before the consequential step. The agent can do the preparation first: gather evidence, check details and propose an action. The reviewer then decides whether that specific action should proceed.
A useful approval request shows:
- What will happen, including the recipient, amount or affected record.
- The source information supporting the action.
- Any missing details, conflicts or exceptions.
- The available choices: approve, edit, reject or escalate.
“Approve this request” is weak if the reviewer must reopen several systems to understand it. The approval screen should make the decision clear without hiding uncertainty.
Approval must also be enforced by the system. An instruction telling the agent to ask first is not a substitute for blocking an unapproved action. If the proposed recipient, amount or message changes after approval, it should be reviewed again.
TEFY's agent builds include approval flows, logging and evaluation on the team's own cases, with simple controls so the team decides what the agent may do.
Loosen controls based on evidence
Do not remove an approval step simply because the agent has been running for a while. Review how it performed on representative cases, including ambiguous requests and exceptions.
Track what reviewers changed or rejected, not just what they approved. Repeated corrections to recipient details suggest a different problem from occasional edits to tone.
A narrower permission is usually more useful than blanket autonomy. For example, a hypothetical team might allow a tested receipt acknowledgement to send automatically while keeping refund promises and complaint responses behind approval.
TEFY's delivery approach includes evaluation against an agreed test set and thresholds before launch.
For your own permission decisions, define what acceptable behaviour looks like and test the proposed change before removing an approval requirement.
Start with an action list
Before discussing a build, walk through one workflow with the person who does it today. List every action, tag its risk group and identify who approves the hard-to-undo steps.
If the team disagrees about a tag, investigate the consequences and the undo path. That discussion is valuable scope work, not a delay.
Once the boundaries are clear, a fit call can help determine whether a scoped agent pilot is the right next step. Start with what the agent may do, not just what you hope it can accomplish.